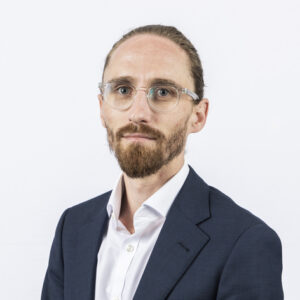
Mark Luckin leads Lockton Australia’s Cyber & Technology Practice, advising organisations on cyber risk, privacy, digital resilience and the insurance implications of technology-related risks. He works with organisations ranging from small businesses to ASX 50 companies, helping boards, executives and risk leaders understand, manage and transfer cyber risk.
With more than 12 years of combined legal and insurance experience, Mark regularly advises organisations on cyber preparedness, governance, incident response and recovery. He has supported numerous complex cyber incidents, including data breaches, ransomware events and regulatory investigations, providing guidance on reporting obligations, threat actor negotiations and insurance response.
Prior to joining Lockton, Mark managed complex claims for a global insurer and worked alongside commercial law firms and barristers. He is a regular contributor to industry publications and conferences and is recognised for his practical, commercially focused approach to strengthening cyber resilience and supporting organisations through an evolving risk landscape.
AI, Privacy and Governance: Practical Lessons from a Real-World Incident
AI can, and will, accelerate care, administration and workforce productivity, but adoption can move faster than governance. This interactive discussion will examine a real, de-identified cyber and privacy incident experienced by an aged care organisation after information was shared with an unsanctioned AI tool.
There was no malicious actor and no conventional cyberattack. The event arose from ordinary, well-intentioned use of emerging technology, making its lessons especially relevant to providers pursuing digital transformation.
Mark Luckin, Head of Cyber & Technology Risk at Lockton Australia, Reece Corbett-Wilkins, Partner and Head of First Response at Atmos, and a representative from a leading cyber insurer will use a hypothetical scenario based on a real incident to explore what can happen when AI creates an unexpected privacy event.
Drawing on their experience supporting organisations through cyber and privacy incidents, they will discuss what was known at the outset, what remained uncertain, which decisions could not wait, and how legal, technical, operational, communications and insurance considerations can be coordinated during a rapidly evolving incident.
Using a practical timeline, the speakers will take delegates from discovery through triage, containment, preservation of legal privilege, assessment of affected information and people, regulatory and notification considerations, stakeholder communications, insurer engagement, remediation and review.
The discussion will reflect candidly on the realities of responding while continuing to provide services, including how to encourage early internal reporting without discouraging responsible experimentation.
The session will translate the experience into practical actions aged care leaders can apply, including:
The discussion will also examine insurance as an integral component of a mature digital transformation strategy. Risk transfer cannot replace sound governance or cybersecurity, but appropriately structured cyber insurance can provide access to experienced advisers, fund eligible response, investigation, notification, restoration and liability costs, and protect financial resilience when an incident occurs.
Delegates will leave with a realistic incident response roadmap, practical AI governance questions for management and boards, and a clearer understanding of how collaboration across legal, insurance and response teams can strengthen digital confidence while protecting the privacy, trust and dignity of older Australians.